What Is The Difference Between Encryption And Tokenization?
However, via relentless efforts and incredible ingenuity, Polish codebreakers, led by Marian Rejewski, managed to make important breakthroughs in understanding the machine’s operation. Their work laid the inspiration for British efforts at Bletchley Park, where a staff of sensible minds, including Alan Turing and his well-known Bombe machine, devoted https://technologytronicspro.com/protecting-data-key-encryption.html themselves to decrypting Enigma-encrypted messages. It allowed Caesar to share confidential army info without the worry of interception or decoding by enemy forces. The cipher was an effective technique of securing communication during a time when encryption techniques were not as complex as they’re right now.
Modern Cryptographic Context

As present techniques and protocols are heavily reliant on conventional cryptographic methods, the shift to post-quantum algorithms requires cautious planning and coordination. Additionally, the efficiency of post-quantum algorithms needs to be optimized to make sure efficient implementation in real-world scenarios. DES was designed to secure digital communications and ensure the confidentiality, integrity, and authenticity of data. It utilized a symmetric key algorithm, which means that the identical key used to encrypt the information was additionally used to decrypt it. With a set key measurement of fifty six bits, DES was extremely regarded for its energy and resistance towards brute force assaults on the time of its introduction.
The United States developed the first-generation Knowledge Encryption Commonplace (DES) within the 1970s to secure sensitive authorities communications. Meanwhile, Soviet cryptographers worked on their categorized systems, partaking in a cryptographic arms race. Spy agencies on either side attempted to interrupt each other’s codes, using everything from brute-force assaults to stolen cipher keys. This historical cryptography methodology was an early instance of transposition ciphers, where letters are rearranged rather than changed. Although basic by today’s requirements, it set the stage for extra superior cryptography and encryption methods.
- Vernam’s model used punched tape, but later purposes typically used notepads, because the prime sheet could be easily torn off and discarded.
- Therefore, the safety of RSA will increase as the scale of the keys and the modulus improve.
- As the system is fairly easy to crack, one other interpretation is that this mechanism is used more for authentication than encryption.
- These encryption strategies use complicated algorithms and keys to guard info, making it just about impossible for unauthorized people to access or alter the info.
- It is imperative to frequently replace and patch communication protocols to mitigate potential vulnerabilities and keep a powerful safety posture.
- Netscape introduced SSL know-how to secure bank card transactions with PKI, but weren’t allowed to export their secure 128-bit version outside the us
The output state array produced by the last spherical is rearranged into a 128-bit output block. Each spherical, the state array is modified by a sequence of operations that embrace byte substitution, permutation, and arithmetic operations over a finite field as proven in the figure under. After the final round, the state array accommodates the encrypted or decrypted information, which are then copied to an output matrix to produce the ultimate ciphertext or plaintext block. While 3DES is slower than DES due to its triple encryption course of, it’s nonetheless considered a relatively fast algorithm and may be carried out in hardware, in addition to software. Additionally, due to its small key measurement, DES is now thought-about insecure 19 and has been changed by the advanced encryption standard (AES). It is a very completely different encryption technique that’s based mostly on utilizing a protracted, randomly generated key that is at least so long as the plaintext.

Caesar Cipher
Homomorphic encryption is one other sort of encryption that enables computation to be performed on ciphertext 38, which implies that information may be encrypted and manipulated without the necessity to decrypt it first. In different words, it enables computations to be carried out on knowledge with out revealing the information itself. This is a big breakthrough in the subject of cryptography as it permits for secure computation and knowledge evaluation without compromising privateness 39. Homomorphic encryption has numerous functions in varied fields corresponding to finance, healthcare, and cloud computing 40. For instance, it can be used to carry out safe knowledge evaluation on delicate data 41, similar to medical records, with out the need to reveal the data to unauthorized events.
2 Homomorphic Encryption
Register for this webinar to hear IBM experts share insights, finest practices and practical strategies for making use of AI, automation and information applied sciences in fashionable enterprises.
]]>
What Is Encryption?
Encryption keys enable encryption to meet its promise of safeguarding delicate information whereas still making certain that the right individuals can access important data. These keys make it attainable to encrypt or decrypt data as wanted — and in the end, they decide whether encryption strategies reach their full potential. A KMS is a centralized platform that manages and regulates cryptographic keys and certificates within an organization. It is crucial for a complete encryption technique to make sure the safe distribution, storage, and revocation of encryption keys and digital certificates.
Forms Of Encryption Keys
Minimize key availability and redundancy, leveraging secure replication of keys throughout a quantity of appliances with automated backups. Utimaco’s Trust as a Service is a cloud-enabled Marketplace that delivers Data Protection, Secure Payments, and Key Management on-line providers. Leverage the cloud to deploy and manage your business whereas having fun with decrease complete price of ownership, smooth integration, and the power to scale immediately.
- Secure key administration practices are crucial, and fortunately, many wonderful options promise to boost overall security and compliance.
- Keys mustn’t ever exist in plaintext exterior a safe boundary.A key in a config file, surroundings variable, supply code, or e-mail is a compromised key.
- Once you adopt a provider’s KMS, shifting workloads elsewhere can be tough.
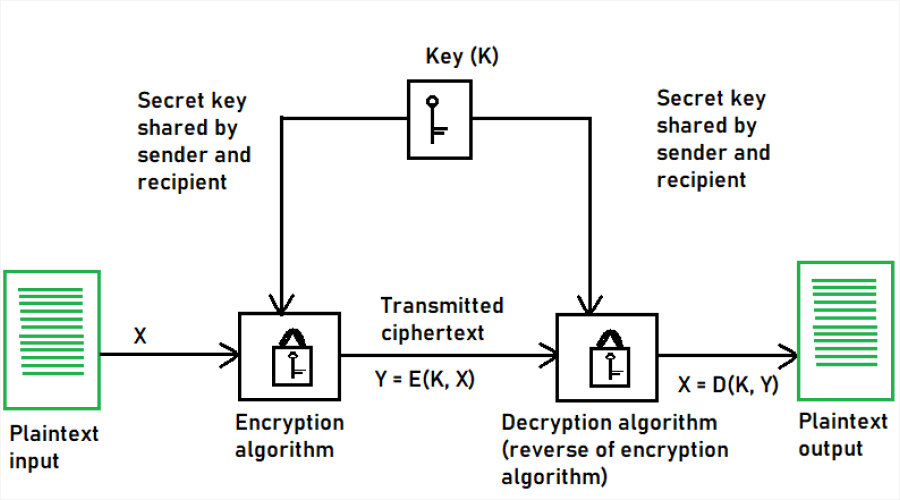
- This course of could additionally be known as a key distribution or key trade.
Able To Safe Your Enterprise?
You must additionally account for compliance necessities, operational realities and, perhaps most significantly, the emerging threat of quantum computing. PQC just isn’t a far-off idea https://sellrentcars.com/developments/what-is-software-as-a-service-saas.html; it’s an imminent shift that enterprises want to organize for now. Hardware Safety Modules (HSMs) handle cryptographic operations within a safe hardware boundary, ensuring that keys never depart the protected reminiscence. Cryptography keys should be stored with a excessive degree of confidentiality, integrity, and availability (the CIA triad). The storage location may not be an active memory however only acquired from an operational memory available to cryptographic algorithms.
Ciphertrust Database Safety
Organizations that want to fulfill strict compliance necessities, corresponding to PCI DSS or GDPR, might select HSM, understanding that keys by no means depart the secure environment. Key rotation entails periodically replacing old keys with new ones. Regular key rotation helps to reduce back the risk of key compromise and restrict potential damage if a key’s uncovered. Key administration methods regularly feature automated key rotation for consistency and safety.
]]>